Keylogger software records everything an employee types, including passwords, personal messages, and financial or health information. Some companies believe employee keystrokes can measure productivity or prevent insider abuse, but keyloggers inevitably capture far more than that and create serious security and legal risks. This article explains what a keylogger does, when it’s legal, how to keep your organization safe from malicious ones, and what to watch for.
What is employee keylogger software and how does it work?
A keylogger (also known as a keystroke logger) is surveillance software that records every keystroke you make on your computer or mobile device. Companies may review employee keylogger software to track user activity or help their IT departments troubleshoot computer issues, but threat actors use the same technology to steal passwords and other sensitive information. Keyloggers can be either:
- Keylogger software
Software deployed to an endpoint that records keystrokes and sends the log records back to an administrator or centralized server. Most keylogger software works on desktops and laptops because Windows is so prevalent in business, though macOS and mobile versions also exist. Capture is managed through an OS-supplied API, kernel hooks, a hypervisor, a web-form script or memory injection. - Keylogger hardware
placed in line between a wired keyboard cable and the computer port, or within the keyboard itself. No software is required, and the keyboard buffer can be accessed within the BIOS. The attacker would need physical access to install it and then retrieve the keystrokes.
Why employers consider employee keystroke monitoring (and why it backfires)
Companies often consider keystroke monitoring for three main purposes: managing employee productivity, high-volume data entry, or catching insider threats. For instance, if you have data entry employees who must meet a certain words-per-minute rate, managers might think a keylogger is the answer. The same goes for security teams searching for insider threats, whose employees have an abnormal keystroke rhythm.
In practice, recording raw keystrokes creates more problems than it solves:
- Data overload: at 40 words per minute, on average, one person typing for an hour will have produced some 2,400 words. That’s a massive amount of unstructured text which no one in the organization can possibly read through.
- Security liability: a keylogger can’t tell the difference between business work and sensitive credentials, so its logs will inevitably contain plain text passwords. In practice, recording raw keystrokes creates far more problems than it solves.
- Words, banking details and confidential records: That makes the monitoring database a prime target for attackers and a serious insider threat if a privileged administrator is to misuse it. GDPR’s integrity and confidentiality principle (Art 5(1)(f)) and the security obligation (Art 32) place the onus of protecting that data squarely on the employer.
- Erosion of trust: In the APA’s 2023 Work in America survey, workers who reported being monitored were more likely to say they were not valued at work (26% vs 17%). A Future Skills Centre study of Canadian workers found that those under intense monitoring (which they defined to include keystroke logging) were more likely to report lower job satisfaction, less trust in their employer, and higher stress. For data entry verification, you only need to know that input occurred; you don’t need to know what the input was.
Is keystroke logging legal at work?
Unlike any other method, keystroke logging records the raw keystrokes typed into all application windows at a level which regulators in Europe and the courts in general would regard as excessively intrusive in an employment context.
- Failure of data minimization (Article 5(1)(c)): Recording every character would collect far more personal data than is necessary to confirm that work is being carried out or to assess efficiency.
- Special category data (Article 9): Keystroke logs will capture health information, political or religious views and other special category data. Article 9 generally prohibits processing such data and permits only very narrow exceptions, none of which cover blanket keystroke capture.
- Security (Article 32): Logs full of passwords and banking details create a duty to protect data the employer never needed to protect in the first place.
- Consent is almost never a valid legal basis (Articles 6 and 7). The Article 29 Working Party’s Opinion 2/2017 on data processing in the context of work (WP249) concluded that given the power imbalance between employer and employee, consent cannot and should not be the legal basis for the vast majority of processing carried out in the course of employment. The European Data Protection Board has taken that position further in its Guidelines 05/2020 on consent, stating that employee consent is permissible only in the most exceptional circumstances where the employee would suffer no adverse consequences as a result of refusing to consent. Member States may also adopt more restrictive employment- specific rules in accordance with Article 88.
Case law: In July 2017, the German Federal Labour Court (2 AZR 681/16) held that findings from a keylogger used in the absence of any specific suspicion of a criminal act or other serious breach of duty could not be used as evidence in a dismissal case. It was a web developer case decided under Germany’s pre-GDPR data protection regime, and Bird & Bird at the time noted that it aligned with WP249. It’s a well-known warning against ‘shot in the dark’ keylogging.
United States: There is no general federal ban. The Wiretap Act (part of the ECPA) prohibits the intentional interception of electronic communications under 18 U.S.C. § 2511. There are two exceptions to that: (2)(a)(i) for interception as part of ordinary course provider activity and (2)(d) for interception with the prior consent of a party. Whether a particular keylogger situation falls within those exceptions depends on the facts, so you need legal advice before you rely on them.
At the state level, Connecticut, Delaware and New York (Civil Rights Law § 52-c) all require employers to give notice of electronic monitoring. Maine’s LD 61 (effective in summer 2026) goes further by requiring notice and imposing substantive limits on employer surveillance.
See our US state-wise employee monitoring laws guide for more detail.
In summary, keylogging is not always illegal; it’s hard to justify, and reasonable, secret keylogging is risky in most jurisdictions.
How to protect your organization from keyloggers
Most keylogger risk comes from attackers, not employers. Malicious keyloggers typically arrive through phishing and run as unauthorized executables or scripts. CISA’s guidance on stopping phishing at the first stage and the joint NSA/CISA/FBI phishing guide point to the same layered defenses:
- Block unapproved software: Application allowlisting stops unknown executables, including software keyloggers, from running on corporate endpoints.
- Keep endpoint protection and patching current: Update operating systems, browsers, and endpoint detection and response (EDR) tools to close the vulnerabilities keylogger malware exploits.
- Use MFA: Multi-factor authentication means a captured password alone is not enough. CISA recommends phishing-resistant methods such as FIDO/WebAuthn where possible, because SMS and voice codes can still be intercepted or phished.
- Physically inspect shared machines: Check shared and public workstations for inline hardware keyloggers between the keyboard and the PC. Software controls will not catch these devices, so routine visual checks and port security matter.
- Train staff to recognize phishing: Teach employees to spot malicious links and attachments before they run unauthorized code.
What to monitor instead of keystrokes
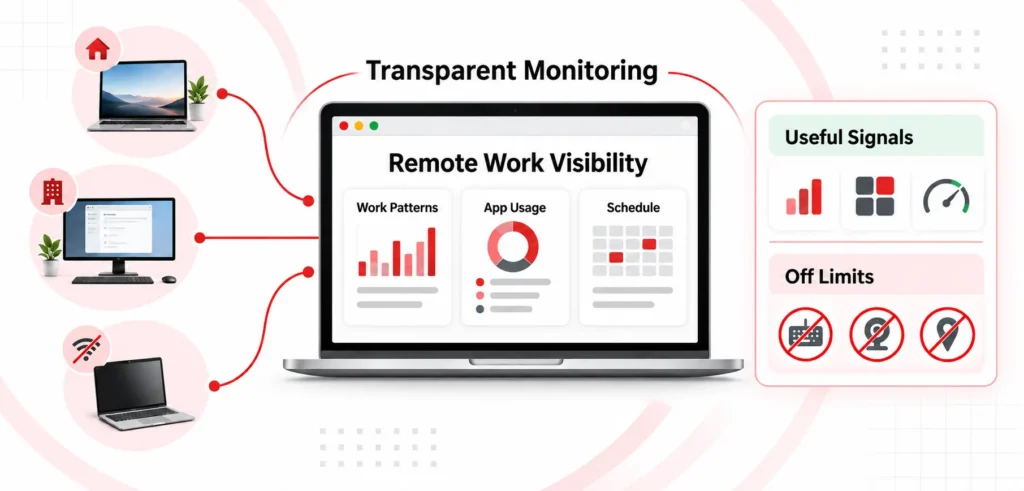
Privacy-first computer monitoring monitors employee productivity and asset protection with objective, sanitized, purpose-restricted activity data, not invasive surveillance. Monitoring with role-based monitoring of applications, role-based monitoring of active/idle time, and role-based monitoring of the apps used on the device, not actual keystrokes or live screen videos.
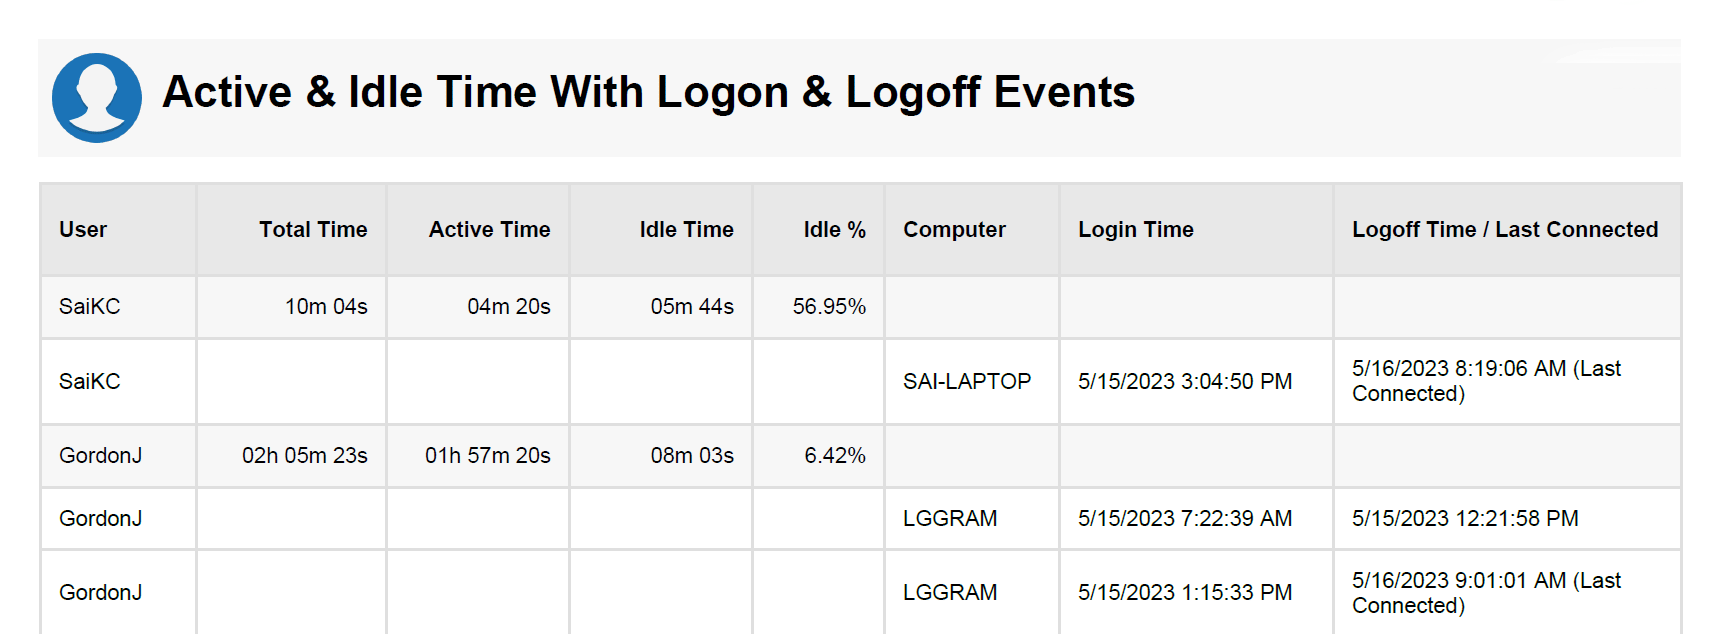
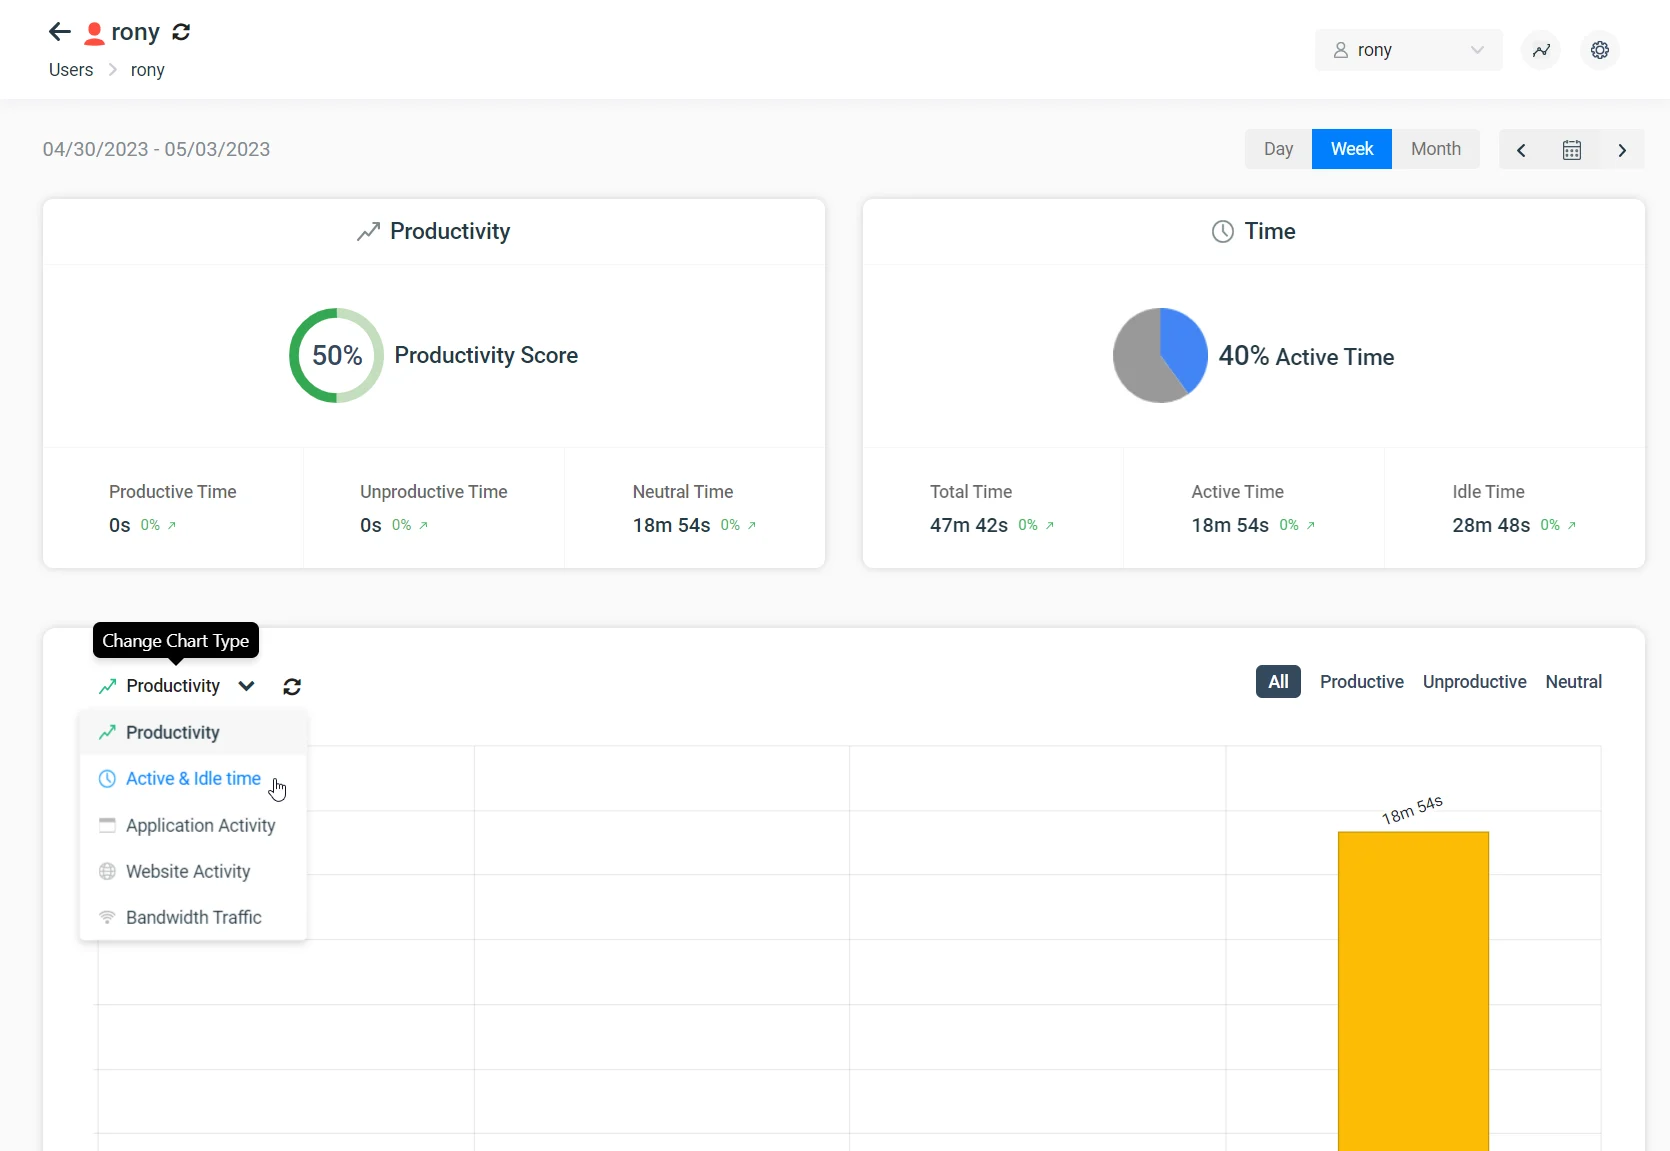
Active vs. Idle Time
Rather than recording which keys were actually pressed, they simply record whether or not there was some form of keyboard or mouse activity during a time window. In the example above, that would be sufficient to confirm there was input during the application usage, without actually recording the records that were entered.
The improved tools will also have an idle exclusion list so that, for instance, a Zoom or Teams call wouldn’t generate a false inactivity alert. They can also perform pattern analysis to detect the kind of fake signals generated by a hardware or software “mouse jiggler” without reading the screen or recording any keystrokes.
Contextual Screenshot Monitoring
Always-on screen recording is a big GDPR risk. Privacy by design disables screenshots unless a high-risk event triggers them under policy, such as opening an approved application or accessing a disallowed URL. Attach delete policies to captures to comply with GDPR’s storage limitation principle (Art. 5(1)(e)); the default might be 14 or 30 days.
Role – Based Access Control and Data Segregation
Workforce analytics should follow the principle of least privilege. Department managers should have access only to team-level aggregations; IT security can view DLP logs; raw session inspection should be limited to organizational data protection officers or joint HR/Legal requests.
App and Website Usage, Work-Hours Scheduling, and Endpoint Controls
Three additional practices address productivity and insider-threat needs for not reading keystrokes:
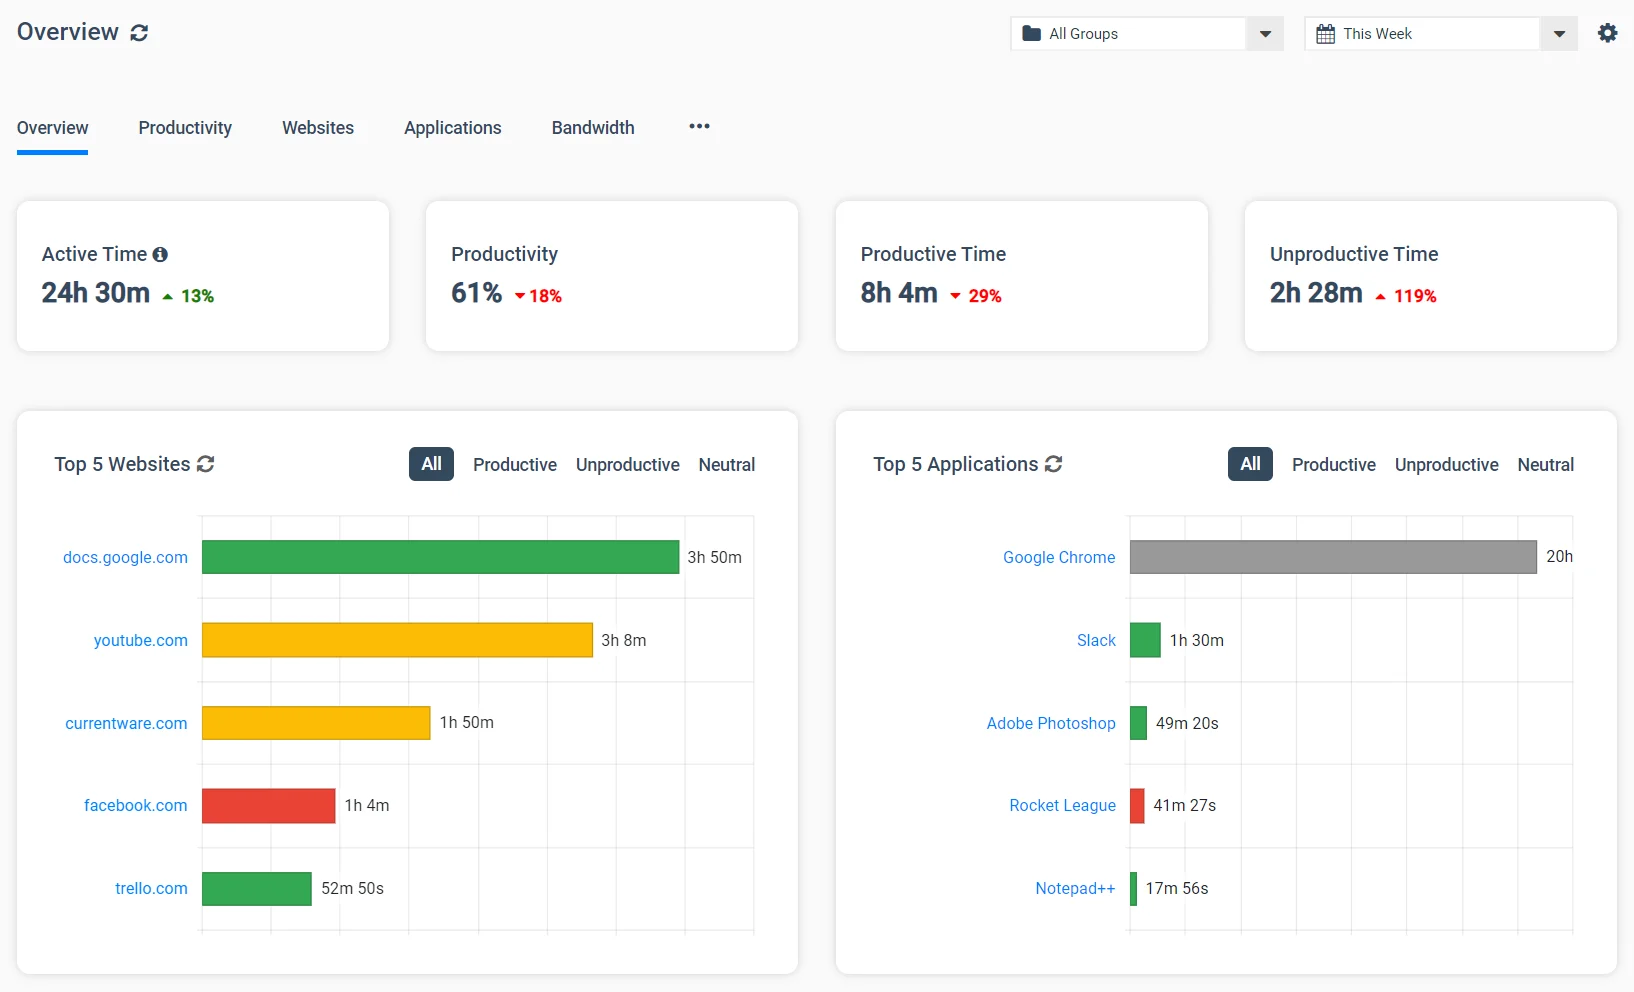
- Use of apps and websites: Record which apps and website domains are used and for how long, rather than the information written inside.
- Surveillance during working hours only: Enforce tracking routines so activity data is collected only during working hours.
- Security controls for insider threats: Deploy USB device control, application allowlisting, and web filtering to block unauthorized file transfers and risky executables directly without capturing keystrokes.
Guardrails and implementation checklist for employee monitoring
When GDPR applies, most employee monitoring software that systematically targets all employees will require a DPIA beforehand, as it forms one of the high-risk factors in the criteria established by the EDPB. Find out more about the other lawful bases and steps for employee monitoring in our GDPR DPIA guide.
Here’s an implementation checklist for putting guardrails around workplace monitoring:
- Define the purpose: Record the particular security or business requirement, like software license right-sizing, enabling data egress, or workload balancing.
- Prioritize the least invasive indications: Identify application in use, URL domain, and on/idle time with no keystroke recording and streaming desktop video.
- Conduct a DPIA if you will have to: Assess need, proportionality and risk to employees’ rights pre-deployment.
- Publish a monitoring policy: Tell employees what data is collected, why, and how it is used with a clear workplace monitoring policy template. In Connecticut, Delaware, New York, and Maine, law requires written notice.
- Limit Monitoring to Work Hours: Configure tracking schedulers to restrict data collection strictly to designated work shifts.
- Restrict access and include retention: Require role-based access control (RBAC), multi-factor authentication (2FA) and automated data retention limits.
- Consult works councils where mandatory: Where you are legally obliged to do so (for example, in countries like Germany with co-determination legislation) you can ensure work council agreements are in place prior to the installation.
- Review regularly: Audit your monitoring configurations, access logs, and retention policies periodically to ensure ongoing proportionality.
How CurrentWare supports keylogger-free monitoring
CurrentWare does not track keystrokes. CurrentWare is a cloud-hosted solution that you can also install on your computer, so you decide where the information is stored. It is privacy – focused and organized into modules that serve a distinct purpose:
BrowseReporter: Monitors active and idle time, application usage and bandwidth consumption. Features trigger-based screenshots (turned off by default), idle – exclusion list for accurate video-call tracking, mouse jiggler detection, and SaaS license optimization dashboards.
BrowseControl: Limits category access. Can also be used to block websites based on category, configured to filter against URL, restrict web file upload/download, and configured to support zero-trust application allowlisting.
AccessPatrol: Delivers endpoint DLP by blocking removable media, allowlisting hardware based on serial number, and logging file activity on USB drives and network shares. Used in conjunction with BrowseControl, these capabilities prevent unwanted cloud uploads that could lead to data exfiltration.
EnPowerManager: Automatically applies PC power schedules and provides an audit of your user logon and logoff history.
With Microsoft Entra ID user sync, macOS support, and schedule adherence deviation reporting, the suite offers businesses real-world workforce telemetry. Watch our YouTube walkthrough of CurrentWare’s employee monitoring software to see how keylogger-free monitoring works in practice.
As Sa’rah Plesner, IT Manager at EHOB, says, “We were looking for an easy-to-use, reasonably priced, and strong enough product to get the information we needed without the invasive aspects such as keystroke monitoring – we want to monitor our people without being Mr. Smith from the Matrix!”
Conclusion
Keylogger software tracks 100 times more than all but the biggest businesses require, transforming the information it collects into a security risk. Activity-level monitoring, a published policy and controls that prevent malicious keyloggers will reveal and protect you from loggers but will not store keystrokes. Regulators and courts find record-high capture overbroad and unreasonable, so mission-based collection and explanation will serve you better: Compliance, security, employee trust.
| Advantages of Keylogger Software | Disadvantages of Keylogger Software |
|---|---|
| Easy to deploy at-scale | Often flagged by antimalware software as malicious |
| Inconspicuous user activity monitoring | Incapable of logging BIOS inputs |
| Can be deployed without physical access to the device you would like to record keystrokes on. |
Keylogger Hardware
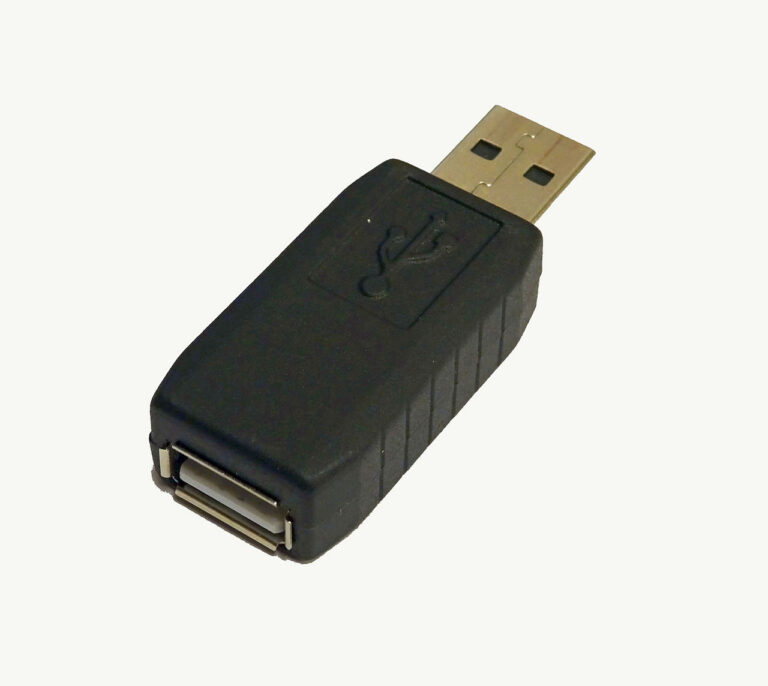
A hardware-based keylogger is typically a peripheral that can be installed in line with the keyboard’s connector. These keyloggers are designed to have an innocuous appearance, making it difficult to detect by users that are not familiar with the devices. A hardware keylogger may also be installed within the keyboard itself, making detection far more difficult.
To access the keystroke log the administrator of the keylogger will typically need access to the computers, making the retrieval of keystroke logs much more difficult to manage when compared to keylogger software.
Unlike keylogger software which can often be detected by anti-spyware software, keystroke logging hardware can only be intercepted by physically removing it from the target computer.
While this type of keylogger is typically a peripheral, there have been other varieties such as a proof-of-concept method where the electromagnetic emissions of a wired keyboard have been captured wirelessly from up to 66 feet away.
| Advantages of Keylogger Hardware | Disadvantages of Keylogger Hardware |
|---|---|
| Does not require any software to be installed on the target user’s computer | Requires direct access to the target device, making remote management impossible |
| Can record BIOS keystroke inputs | Typically needs to be installed in-line with the keyboard, making it easy to detect |
What Are Keyloggers Used For?
Maliciously Logging Sensitive Records
Although there are many legitimate cases for the use of keyloggers, the technology is more commonly known for its use throughout the cyber-criminal underworld. In fact, 60% of phishing scams contained some form of keylogging technology, making keyloggers one of the most widely used tools in malware attacks.
Threat actors will use keylogger programs to collect sensitive records such as passwords, payment information, and personally identifiable information (PII). This information may be used to escalate an existing attack or enable attacks from other threat actors.
Also Read: An Overview of Ransomware Attacks: Trends and Threats
Insider Threat Detection
A 2020 report from IBM and ObserveIT found that insider threats cost organizations $11.5 million on average. This is a 30 percent increase from 2018, indicating that insider threats are becoming more and more prevalent in business.
High-security organizations such as those in the national defense industry may monitor their employees for signs of insider threats with keyloggers. They can use a keylogger to detect anomalous behavior such as a WPM cadence that far exceeds what is typical (a potential indicator of a malicious script executing) or the presence of high-risk keywords.
Evaluating Data Entry
Data entry positions require the worker to input a high volume of data from multiple sources into a database. Generally, the information inputted into the database contains customer and account information in the form of alphabetic and numeric information that is entered through the keyboard.
Given the demand for a high volume of data entry from their employees, many companies opt to monitor employee productivity through keyloggers. By capturing the volume of data entered into the database through the employee’s operating system, managers can determine whether or not individual workers are hitting their quota.
As most data entry jobs require a minimum of 45 words per minute entered into the system, an employer can utilize keylogging technology to ensure that its workers are maintaining this standard of production.
To reduce the cybersecurity risks of logging keystrokes an organization may opt for a keylogger that does not monitor individual keystrokes. Instead, they may use software that simply detects whether or not any input was registered.
Also Read: Are You A Victim of Facebook Fatigue?
Productivity Monitoring
Productivity monitoring is a focus in most businesses. Businesses that want to monitor productivity may monitor internet activity, record keystrokes, take screenshots of desktops, or track idle time.
With as much as 64% of employees visiting non-work related websites every day at work, employers are often incentivized to implement tools that detect disengagement.
That said, recording individual keystrokes puts the company at risk of capturing sensitive personal information such as private messages and passwords.
With keyloggers, employers can see every last keystroke that their workers are typing. While this could theoretically be used for productivity monitoring, the sheer quantity of data and the potential to capture sensitive information make a keylogger an ill-advised method for monitoring employee productivity.
So, what’s a better way to prevent employees from wasting time at work?
Employee internet monitoring software is the perfect solution for recording the websites that employees visit, tracking what apps are used, and evaluating how much time is spent on activities that are considered productive for your organization.
When employers monitor productivity, they are often looking for behaviors that are considered to be unproductive such as spending time playing games, browsing social media, or engaging in other activities that do not directly benefit the business.
Rather than taking the risks that come with capturing individual keystrokes, internet monitoring software offers a privacy-conscious option for enforcing acceptable use policies and monitoring user activity.
Concerns With Keyloggers
Legal
Monitoring individual keystrokes is highly invasive. As these employee monitoring methods risk directly capturing sensitive personal information employers are seldom justified in using them over less-invasive methods such as computer activity tracking software.
Naturally, the legality of recording individual keystrokes will vary from one jurisdiction to another. As a best practice employers must evaluate other options to determine whether or not they truly want to monitor keystrokes or if their goals can be met with less invasive monitoring methods.
Even in jurisdictions where keyloggers are permitted, how the logs are handled can raise legal concerns. Since keylogging technology can capture sensitive information such as a user’s passwords, private messages, or other forms of personal information, this data must be adequately protected from misuse with administrative and technical safeguards.
For example, if an employee is unaware of the keystroke logger, they may reveal personal information via a chat or email with a family member or friend. This type of information can be highly sensitive, and if mishandled, can lead to legal consequences for the administrator.
Also Read: What is a Data Breach? (Infographic)
Data Overload
The average typing speed is around 40 words per minute (WPM). If a given user is writing for an hour straight they will output an average of 2400 words for each hour they write.
Times this by the number of employees in the organization and it’s immediately evident that a keylogger is going to generate ludicrous amounts of data; far more than is useful in most circumstances.
While the actual storage space required for keyloggers is negligible, from a logistics standpoint the sheer volume of information is overwhelming for administrators to effectively manage and interpret.
While artificial intelligence can be trained to interpret this data, this level of sophistication far exceeds what an average business truly needs in an employee monitoring solution. For example, if a business wants to see how much time is spent browsing the internet they can simply use internet monitoring software to run a report on the employee’s internet activity.
Cybersecurity Risks
The databases of keyloggers are an attractive target for hackers as credit card information and passwords are highly valuable commodities within the cybercriminal underworld.
From an insider threat management perspective, a disgruntled administrator with access to the logs is a significant threat. They could opt to sell the records to an external threat actor or simply browse the logs for passwords and other sensitive information.
Also Read: BrowseReporter Employee Monitoring Software
Throughout this article, we have touched on the practical usage of keyloggers while also highlighting the many flaws that the technology inherits.
Considering the legal and administrative concerns that arise with the implementation of keyloggers, along with concerns regarding the practical effectiveness of the technology, monitoring software alternatives should be examined by businesses looking to increase security and improve productivity.
The most effective way to improve employee productivity and increase network security is through the use of employee computer monitoring software.
BrowseReporter is an easy-to-use solution for tracking the productivity and efficiency of individual employees or an entire workforce. Its computer usage reports can track internet activity and application usage, providing managers with the insights they need to make data-informed productivity management decisions.
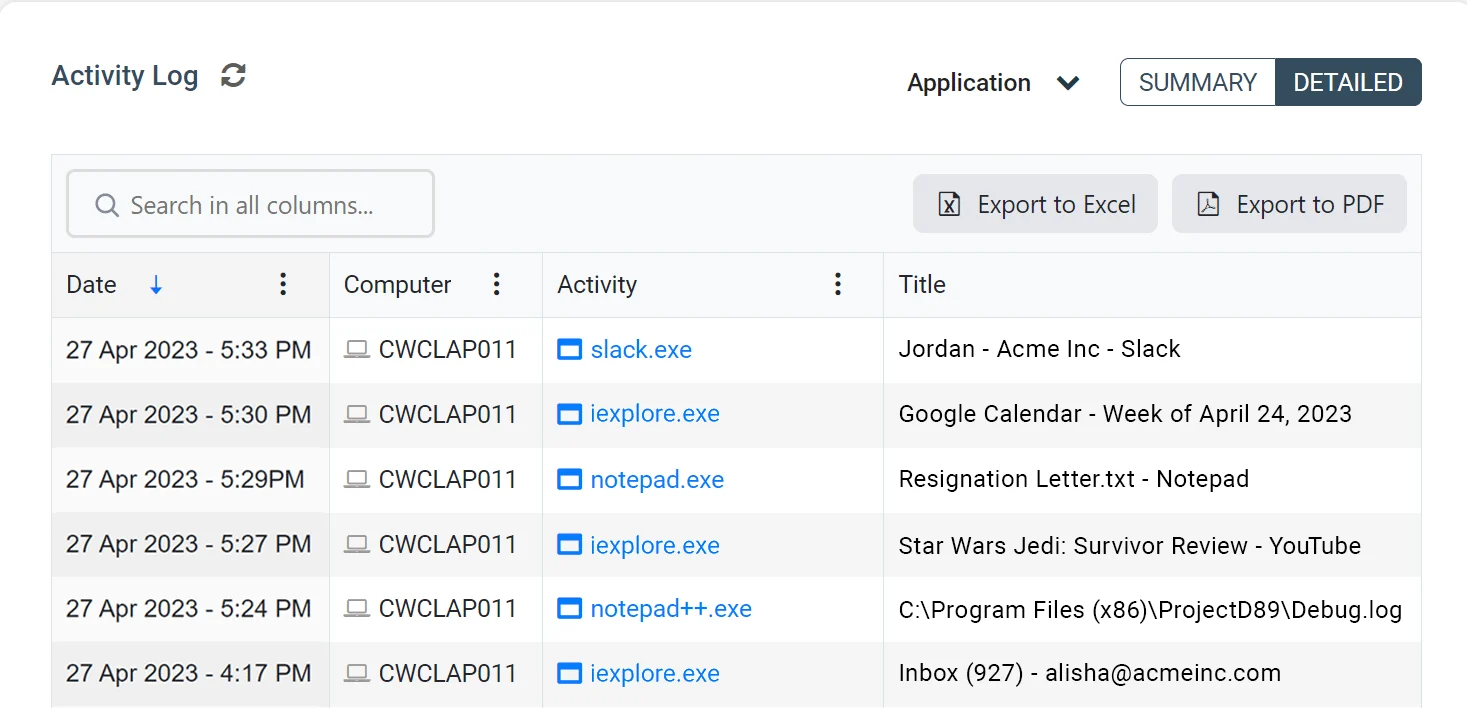
These reports automatically filter out noisy background data such as CDNs, giving an accurate and easy-to-understand overview of employee computer usage.
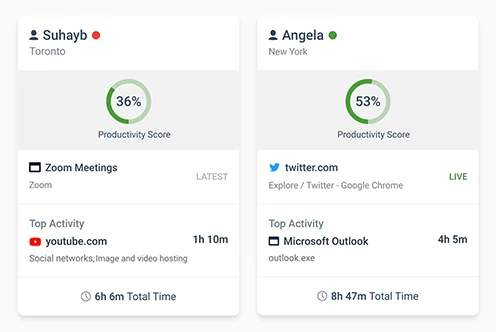
BrowseReporter can be easily accessed by administrators through the central web console, providing convenient access to the records of your entire workforce.
Improve Employee Productivity With CurrentWare’s Remote Employee Monitoring Software
Ready to get advanced insights into how your employees spend their time? Reach out to the CurrentWare team for a demo of BrowseReporter, CurrentWare’s employee and computer monitoring software.
- Improve Productivity
Track unproductive web browsing and idle time to detect time-wasting - Save Time With Intuitive Reports
User-friendly reports make it easy to understand employee computer activity - Enhance Visibility
See how employees spend their time—even on Terminal Server and Remote Desktop Services!
Frequently asked
Frequently Asked Questions:
-
Keylogging is not automatically illegal everywhere, but ungrounded keylogger collection is hard to defend as proportionate, such as under the GDPR, and Germany’s Federal Labour Court did not accept keylogger evidence that was collected without specific suspicion. In the United States, Connecticut, Delaware, New York and Maine all require employers to notify employees of electronic monitoring, thus rendering silent keylogging extremely risky in most places.
-
Some do, but many avoid it because they will be logged by the keylogger: accounts passwords, personal messages, protected health data, bank account data, and more. Instead, many companies will implement employee monitoring tools that monitor application use, website domains, and active vs. idle time.
-
Generally, an employer can view the specific keystrokes you type only if they utilize keystroke logging, screen recordings or screenshots, or applications that examine email and chat content. Privacy-respecting monitoring tools are able to view only whether keyboard or mouse activity was present and which applications or websites were visited.
-
An endpoint-based software keylogger (typically on Windows) operates in the background and intercepts keystrokes using either the OS API, Kernel hook, or memory injection to grab the keystrokes before they are passed along and transmits the recorded text to a server. Hardware keylogger – The hardware type is a physical connector that is attached inline between the PC port and the keyboard cable.
-
Absolutely. Managers only need a handful of basic metrics: Time spent in the app or website vs time idle, which apps or websites are used, whether employees cover their shift, and whether the software you’re paying for is actually being used. The only thing those don’t include is what anyone is writing, but toss in actual productivity metrics, such as, tickets closed, and the picture is all there.