Where web access goes unmanaged, distractions at work cost companies roughly 26 workdays per employee each year and expose their networks to security threats and compliance risks. Today’s web platforms hold your attention using algorithmically driven feeds, autoplay media, and ongoing notifications that disrupt concentration.
IT managers, HR executives, and business owners face three concrete problems: Which websites should be blocked? How can the policy be enforced on laptops which do not always connect to the office network? And how can this be achieved without damaging trust?
This blog includes all three aspects: a tiered blocklist, a policy matrix, research into the costs of distraction, a comparison of the various filtering options, and a five-step rollout plan.
Key Takeaways
- Block websites in three levels: security risks, productivity drains, and bandwidth or data liabilities
- Use category filtering; individual URL lists expire within a few days.
- Both full-tunnel VPNs and DNS filtering leave holes on the remote device, and the NSA has warned that browsers can get around DNS-based protection through encrypted DNS. Endpoint-level filtering fills that hole.
- Use role-based rules and schedules so the marketing team, the purchasing team, and even the recruiting team can keep functioning.
- Issue an Acceptable Use Policy in order to make sure that all blocks are transparent and justified.
Which Websites Should be Blocked at Work?
Block at least three levels of websites on any corporate device, since tiers help keep your policy from becoming too broad and limiting your company’s online activities.
Always Block Security and Compliance Risks
These are sites you would want to be unavailable from your every device, at every hour:
- Phishing sites
- Identified malware distributors
- Adult and/ or explicit content
- Illegal streaming services
- Uncontrolled file sharing networks
This level is about preventing breaches and lowering your legal liability, not concerned with productivity.
Major Productivity Drains
These sites are legal and almost harmless in moderation – but they are designed to be addictive:
- Rolling feed posts: Reddit, TikTok, Instagram, X (Twitter), Facebook
- Entertainment streaming: Netflix, Twitch, YouTube for recreational use
- Internet betting sites
- Web games
During core working hours most organisations do not permit this, but at lunchtime or after a shift the rules are more lenient.
Bandwidth & Operational Liabilities
The second level includes sites that could be a drain on infrastructure or pose a threat to company information:
- High bandwidth video and audio streaming
- Online retail flash-sale portals during shift hours
- Information relating to customer data, source code, or strategy documents which is used in a chatbot that has not been approved or examined is no longer under your control.
Once an employee pastes customer data, source code, or strategic documents into an unvetted chatbot, that information is no longer under your control.
Top Distracting Website Categories to Restrict
For IT teams, it would be impractical to block each URL individually, since every day a large number of new domains, subdomains, and mirror sites are created. In order to properly manage the huge number of new domains, IT teams should introduce category-based web filtering to group the domains together:
- Social Media and Online Forums: Reddit, TikTok, Facebook, Instagram, and X (Twitter) are the most dangerous for time-wasting voluntarily from the user side on account of their infinite scrolling algorithms.
- Video & Audio Streaming: Streaming services such as YouTube, Netflix, Twitch, and Disney+ require a large amount of corporate bandwidth and are a massive distraction from work.
- Online shopping & E-Commerce: Stores such as Temu, Shein, Amazon, and eBay hit major traffic peaks on sales and shopping days, usually during regular business hours.
- Web Gaming and Gambling: Browser games, sports-betting sites, online casino gaming sites, and social community venues all lead to serious productivity drains, along with a high level of legal and compliance risk.
- News, Sports, and Tabloids: News portals and sports updates are viewed at high speed. This can require frequent back-and-forth switching between windows or tabs.
- Shadow IT and Unsanctioned GenAI: Consumer AI chat tools and third-party SaaS apps threaten to undermine organizations’ operational focus and potentially leak corporate IP. A dedicated tool, like AI Usage Insights, can address these risks by tracking and containing generative AI use.
- High Risk Security Categories: Phishing sites, adult/illicit sites and proxy/anonymizer sites should be disabled indefinitely on all hardware owned by the company.
The following policy matrix provides a quick reference for structuring category rules:
| Website Category | Common Examples | Primary Organizational Risk | Recommended Policy |
|---|---|---|---|
| Security & Explicit | Malware sites, adult content, proxy bypassers | Data breach, malware infections, legal liability | Strict 24/7 permanent block across all endpoints |
| Social Media | Reddit, TikTok, Instagram, X (Twitter), Facebook | Focus fragmentation, lost billable hours | Block during core hours; allow during scheduled breaks |
| Media Streaming | YouTube, Netflix, Twitch, Disney+ | Bandwidth saturation, sustained attention loss | Category block for general staff; allowlist work channels |
| Online Shopping | Amazon, eBay, Temu, Shein | Personal errands during work shifts | Block during core hours; allowlist procurement team |
| Gaming & Betting | Browser games, online casinos, sportsbooks | Severe productivity loss, legal non-compliance | Strict 24/7 permanent block |
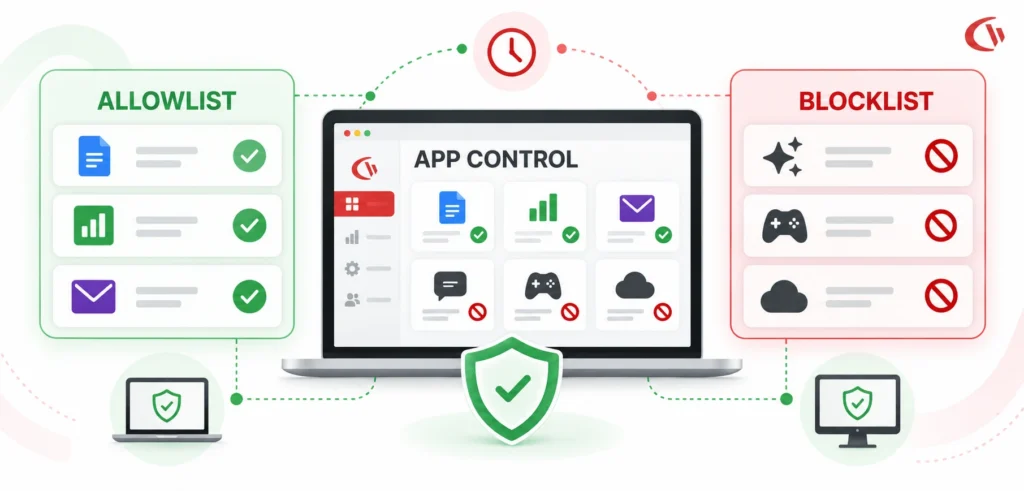
| Shadow IT & GenAI | Unvetted AI chat tools, cloud drives | Proprietary IP leakage, data privacy breaches | Allowlist approved AI tools; block unvetted services |
The Business and Cognitive Cost of Workplace Distractions
The effects of taking breaks from work extend well beyond those mere seconds involving only a few clicks. In a research headed by Dr.Gloria Mark at the University of California, Irvine, work that had been interrupted, for example, by checking emails – was resumed on average after 23 minutes and 15 seconds, typically following two other tasks (Gallup interview). The continuous switching back and forth between work-related activities and social media drains our cognitive resources and hinders deep work.
This results in a substantial loss of efficiency. A 2018 survey of 645IT professionals by Spiceworks, in companies with internet access, found that 58% of employees lost four or more hours each week (that is, 26 full working days per year) browsing the internet for non-work-related purposes. The survey also showed that IT departments introduce filtering mainly in order to:
- Malware and ransomware protection (90%)
- Restricting inappropriate content (84%)
- Preventing unacceptable employee behavior (83%)
- Mitigating legal liability and meeting compliance standards (66%)
- Protecting confidential and sensitive business data (57%)
How to Block Distracting Websites on Distributed Laptops
Traditionally, organizations forced web policy compliance by forcing all remote traffic through full-tunnel corporate VPNs, or by pushing out local DNS resolvers. Full-tunnel corporate VPNs significantly increase latency for cloud apps, and DNS-level filtering is easy to circumvent with modern browser standards like DoH (DNS-over-HTTPS). For a detailed architectural breakdown, see our guides on web filtering for remote workforces and managing encrypted DNS traffic.
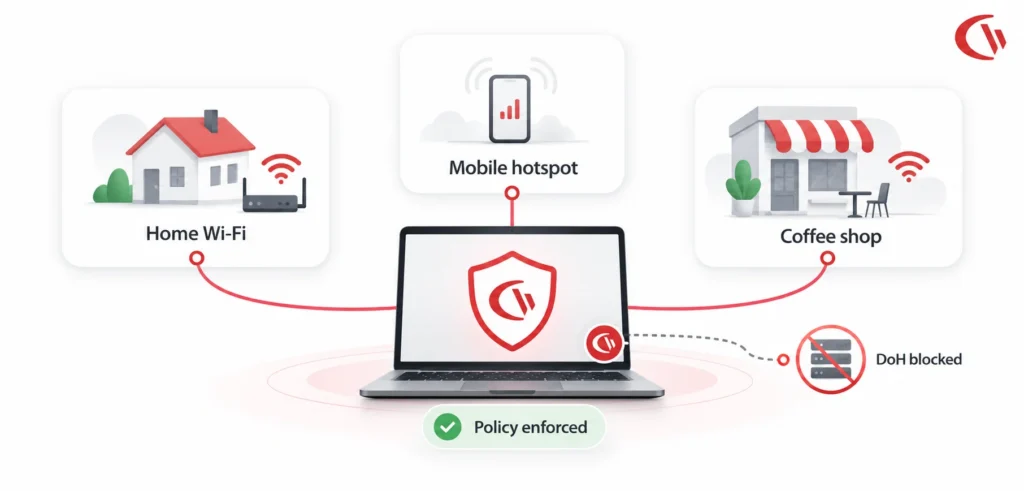
The most reliable solution today is endpoint-level web filtering. Because they don’t rely on a domain name, they enforce policies at the network stack level by running a small agent locally on the device’s OS, whether the employee is on the corporate network, on home Wi-Fi, or completely disconnected.
| Evaluation Metric | Full-Tunnel VPN | Cloud DNS Filtering | Endpoint Filtering (e.g., CurrentWare) |
|---|---|---|---|
| Enforcement Point | Central corporate gateway | External DNS resolver | Local OS-level client agent |
| Network Overhead | High (backhauls traffic to datacenter) | Low | Direct-to-internet (zero gateway backhaul) |
| Off-Network Protection | Fails if user disconnects VPN | Inconsistent on captive portals | Enforced on and off network (including offline) |
| Encrypted DNS (DoH) | Bypassed under split-tunnelling | Vulnerable to browser DoH | Not affected by browser-level encrypted DNS |
| Application Control | No | No | Built-in desktop application blocking |
The endpoint model’s key advantages are consistent enforcement and low overhead. Traffic goes straight to the internet instead of detouring through a data centre, and the policy travels with the device.
Step-by-Step Implementation Guide
Organizations can configure granular web filtering with centralized browser control management like Current Ware Browse Control. The five-step process above applies to most endpoint filtering applications.
Step 1: Decide Deployment Model
Set up the management console, so that it matches your environment. CurrentWare offers managed cloud hosting as well as self-hosted hosting on-premises or in a private cloud (using AWS or Azure). With a self-hosted deployment, your corporate browsing data stays within your private infrastructure, so you maintain full data sovereignty. This is important for organizations with strict data residency or privacy requirements.
Step 2: Deploy the Client Agent
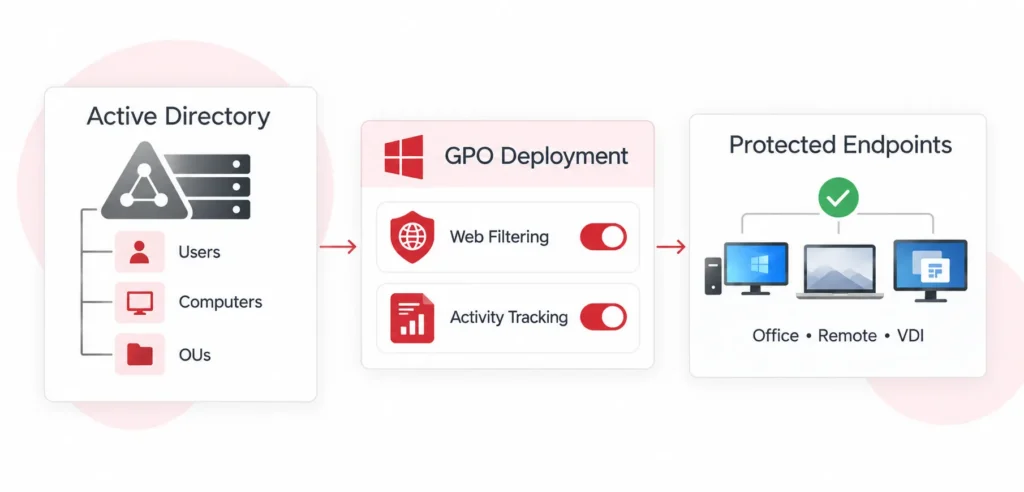
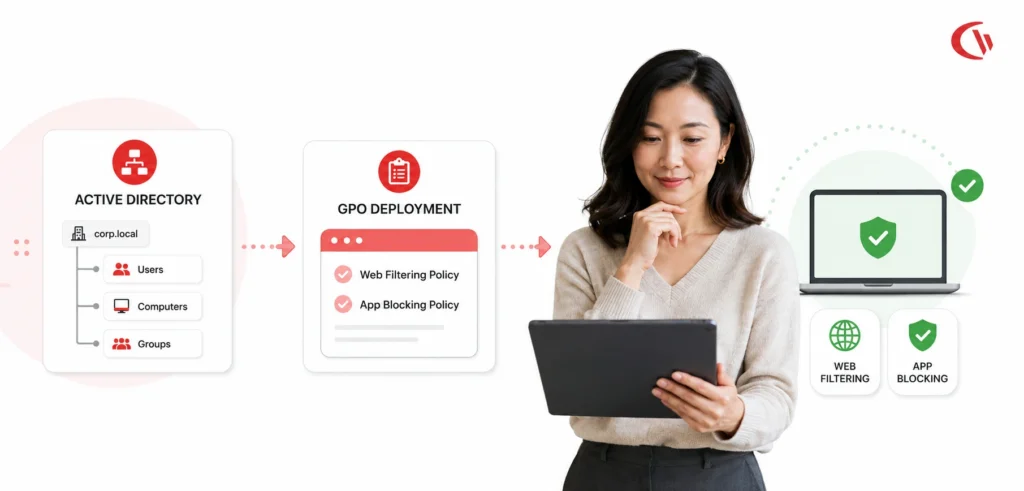
Deploy the lightweight agent to Windows and macOS end-points using common tools:
- Microsoft Intune
- Active Directory Group Policy (GPO)
- PDQ Deploy
- Silent executable packages
Nearly all IT teams already use one of these, so expansion typically doesn’t require additional hardware purchases.
Step 3: Synchronize Organizational Groups
You can import user and device groups using Active Directory or Microsoft Entra ID Sync; by mirroring your departmental hierarchy, policies align with the company structure, and new employees automatically receive the right rules.
Step 4: Define Filtering Rules and Category Blocks
Set up policies for each department by using category filtering, custom URL blocklists, and application restrictions. Arrange for the rules to be in effect during core business hours and to relax the non-security restrictions during lunch breaks. Begin with the policy matrix listed above and then adjust it based on each team’s feedback.
Step 5: Distribute an Acceptable Use Policy (AUP)
Make it clear to employees what constitutes acceptable use of computers and the internet. The Internet Use Policy Template that we provide can help you to set out your expectations in a formal way and at the same time comply with workplace privacy standards and regulatory compliance requirements. Employees are much less likely to feel resentment towards a restriction that they understand than one that is imposed without explanation.
“When designing web filtering for distributed teams, the goal must be seamless, low-overhead protection. By processing filtering rules locally on the endpoint operating system, administrators can enforce security and acceptable use without routing high-bandwidth traffic through VPN bottlenecks.”
— Rony Joseph, Head of Development at CurrentWare
Best Practices for Blocking Distractions Without Harming Morale
Restricting websites requires a balanced approach to ensure policies do not stifle legitimate business workflows or damage employee trust:
- Apply role-based access: By creating a single rule for all, marketing requires access to social platforms while purchasing needs access to e-commerce. A single rule applied to all situations seldom succeeds.
- Make use of the Scheduled Policy Timers: this will allow access to non-malicious entertainment or personal websites during scheduled lunch breaks or after the normal working hours.
- Set up informative block pages: Configure custom block screens which clearly state that the domain has been restricted due to company policy, including a link to an administrative contact for any legitimate requests to override the restriction.
- Alternative solutions for individuals: Those knowledge workers who want personal control rather than having corporate IT management can use individual blockers such as Cold Turkey or Freedom to block or restrict distractions when carrying out specific tasks. These tools suit freelancers and other self-managed workers, but not centrally managed teams.
Legal & Privacy Considerations
As long as employees are aware of the rules, employers can generally control what staff do when using work computers and networks, although privacy laws impose extra restrictions when such tools collect personal information.
Use the UK as an example. The law in the UK, as set out in the legal analysis of ICO’s 2023 guidance, is that the use of new technology to monitor workers does not breach data protection law; an organization must have lawful grounds and respect individuals’ privacy rights. The ICO advises organizations to speak to employee representatives on the measures they intend to use and implement and warns of creeping scope, or scope creep in monitoring, ACCA has summarized.
Three Habits keep you grounded everywhere:
- Make it transparent by explaining what is being blocked, the reasons for this blocking, and what data, if any, is being collected.
- Collect only the stuff that is necessary. It is possible to block even if you have only a very limited amount of personal data. The plans for reporting applications should be carefully scoped.
- Explain your reasoning and keep a written record outlining the business reasons for each policy.
The rules differ from country to country and from state to state, so it’s advisable to consult a qualified employment attorney and/or a privacy attorney before putting them into effect.
Common Mistakes to Avoid
- Excessive aggression in blocking, in general YouTube or LinkedIn may prevent your teams from accessing training videos, product webinars, recruiting channels, and so on.
- Determining from URL lists. Manual lists get outdated. Start with the categories.
- Do not publish the policy document. Enforcement seems arbitrary without an AUP and may even create legal exposure.
- Overlooking remote workers. Using a policy that functions only on the office network does little to secure the majority of the hybrid workforce.
- Even if we decide to use filtering as the entire strategy. As Spiceworks’ own analyst put it, it is just “one layer of many”.
- Just set it and leave it. Since new platforms and AI tools are constantly being released, you should continually check your categories.
Frequently asked
Frequently Asked Questions:
-
No, it isn’t easy. Even private browsing modes and unmanaged VPN programs can circumvent browser extensions and router-level DNS blocks. Nevertheless, endpoint-based filtering software such as CurrentWare BrowseControl implements policies at the operating system’s network stack level for all browsers. Administrators are able to also block unauthorised VPN and proxy executables by means of application blocking.
-
This depends on each department’s responsibilities; although general entertainment video streaming uses a lot of bandwidth, websites such as YouTube and LinkedIn often provide important industry tutorials, product webinars, and recruitment channels. It is recommended that category-level blocks apply to general staff, while specific business-critical channels or departments are allowed.
-
In most places, employers are legally allowed to put restrictions on the use of the internet on company-owned equipment and network policies are clearly set out in an Acceptable Use Policy. Employers operating in areas with strict data privacy laws (for example, under the GDPR in Europe) should communicate transparently and avoid collecting any personal employee data that is not necessary.
-
Website blocking (for example, BrowseControl) is a preventive measure which prevents access to unauthorized websites before the pages are loaded. Employee monitoring software (for example, BrowseReporter) is an analytical tool that records overall application usage, active working time, and operational trends to help managers identify workflow bottlenecks.
Conclusion: Creating a Focused Digital Workplace
Minimizing digital interruptions and protecting corporate devices does not require restrictive micromanagement or cumbersome network hardware. By combining endpoint-based category filtering, scheduled access rules, and explicit communication, organizations can develop a focused and secure work environment across both office and remote teams.
To explore how centralized endpoint filtering and application control can protect your organization’s productivity, learn more about CurrentWare BrowseControl.